Published: November 2, 2026
Just because you're using a European AI provider like Mistral doesn't mean that your data, or your customer's data is routed safely through Europe.
As you can see below, providers like Mistral have a global endpoint (api.mistral.ai) and specific regional endpoints like (api.eu.mistral.ai or api.us.mistral.ai).
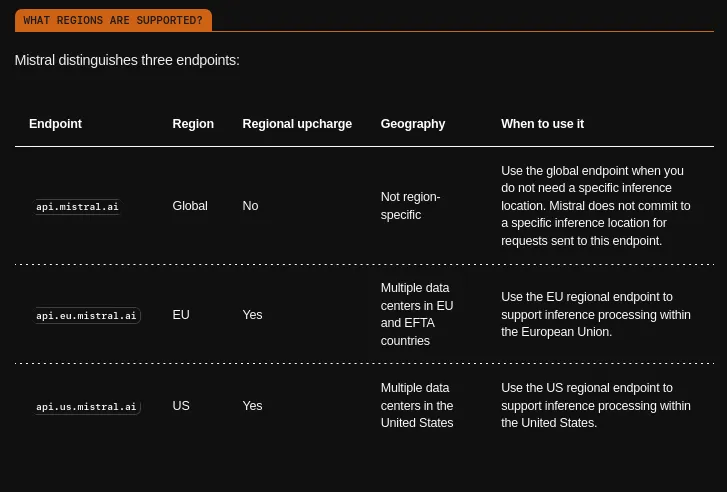
No matter how much value is given to European sovereignty within the organization most developers (or their vibe-coding tools) will pick api.mistral.ai, and as a result your organization's data is not guaranteed to stay within Europe.
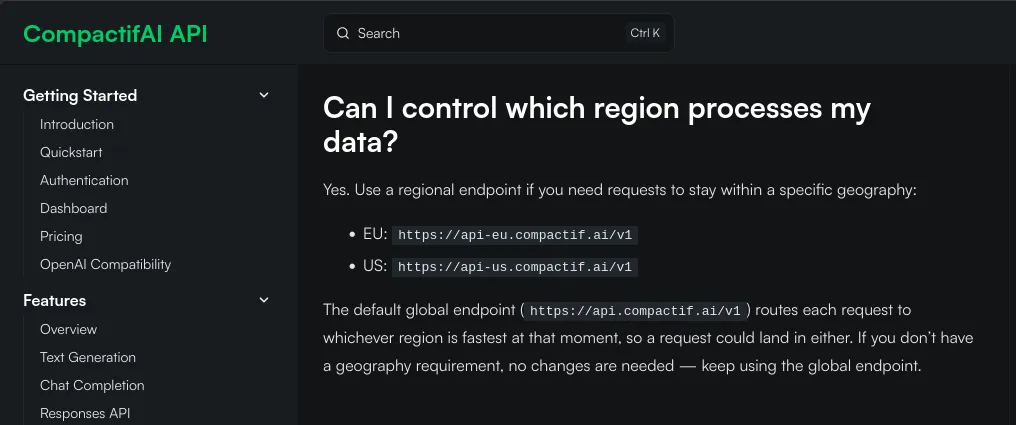
And it's not just Mistral though! Here you can see the same problem with another EU-AI provider (Multiverse Computing):
Not exactly. It all depends on your own Mistral/EU-AI settings (if you use your own API key), or if you have a software vendor/partner (like us) it will depend on their Mistral/EU-AI settings.
This is for example how our Mistral settings look like for EUAIWorkspace:
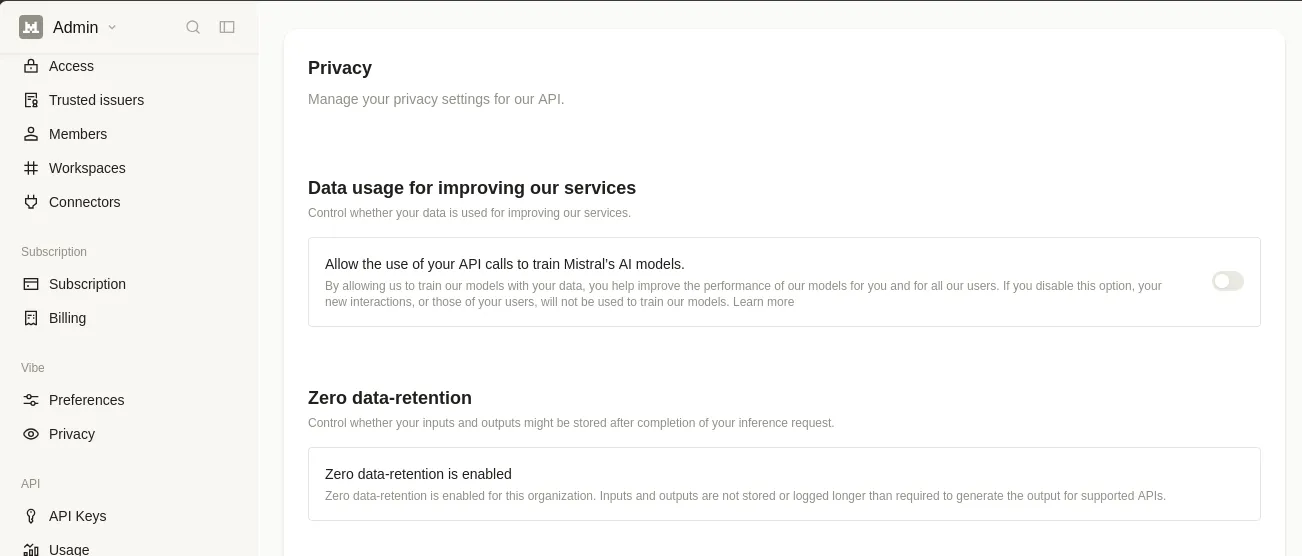
We have explicitly disabled training, and have a special ZDR (zero data retention) account, so exact chat inputs/outputs are not even stored on their servers.
A European provider does not automatically keep your data private or within Europe. Global endpoints are the default, and as a result your data leaves the region without warning.
True European sovereignty requires deliberate care & configuration.
 EUAIWorkspace